Open Source
Core database access workflows, free to use.
€0
Free to use.
Included in Open Source:
- OIDC and LDAP SSO
- Single-query review and approval
- Time-limited browser sessions
- Role-based connection access
- Basic audit log
- Slack notifications
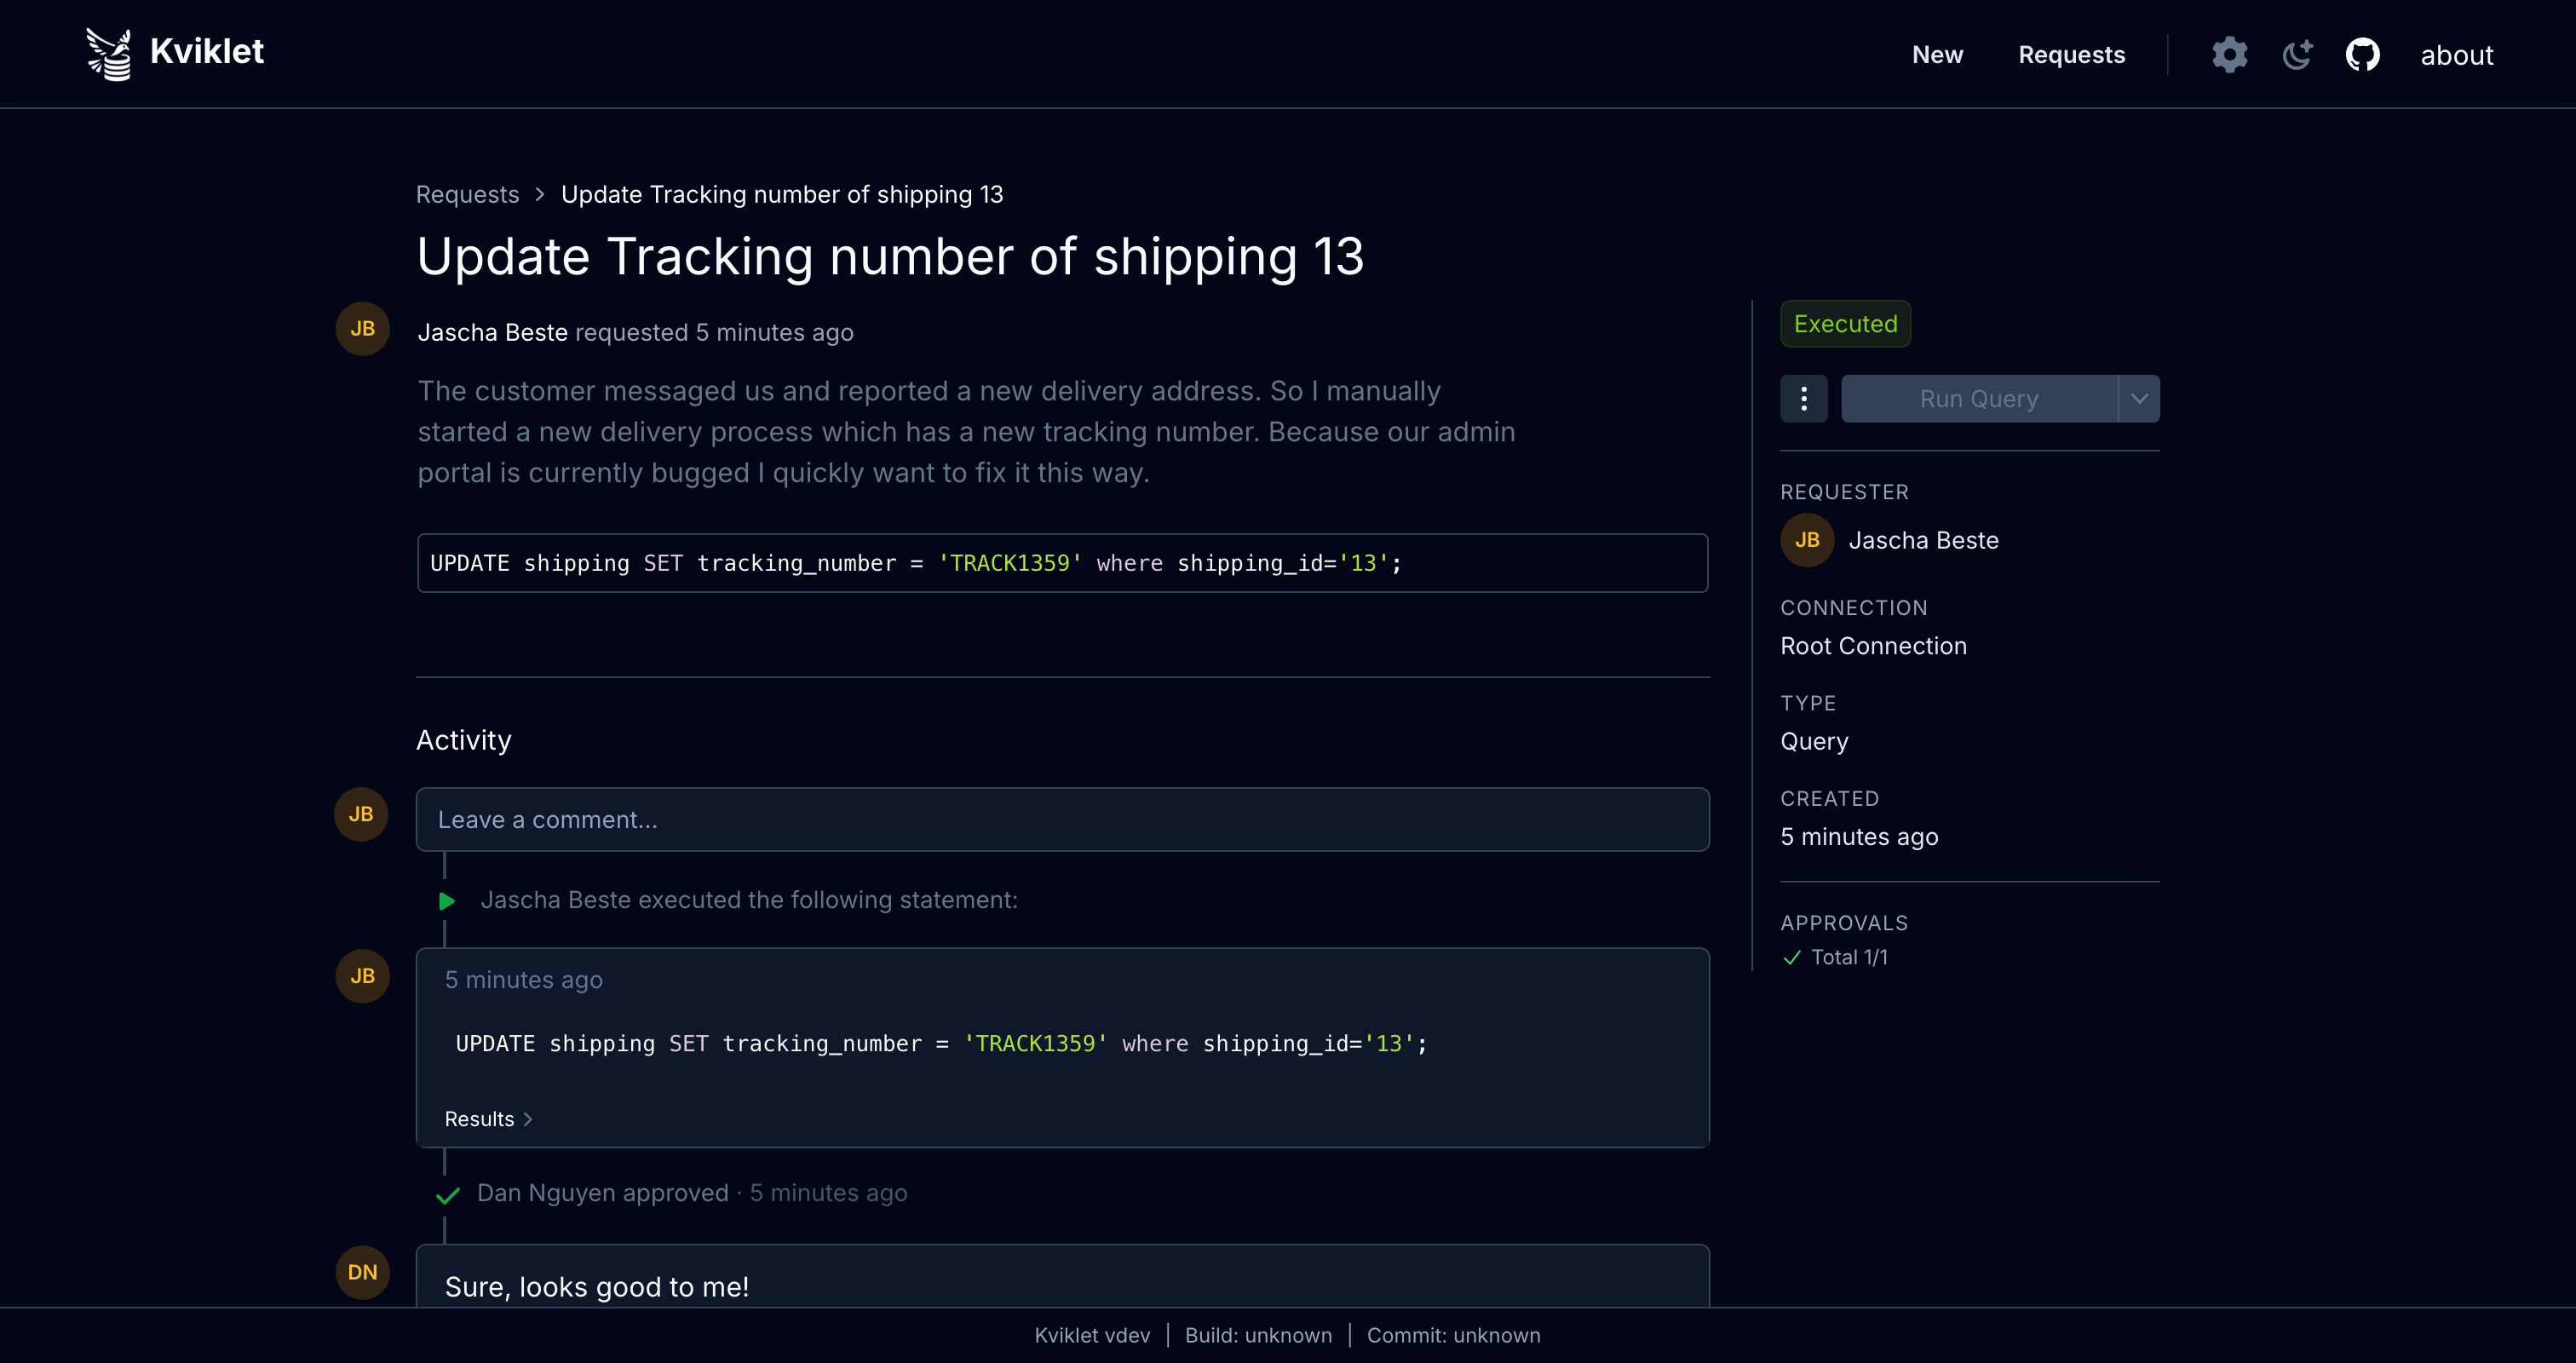


Interactive demo
Try Single Query or Access & Proxy to request, approve, execute, and inspect database activity.
Choose Single Query or Access & Proxy below to begin.
Want a walkthrough for your team?
Request, approve, execute, and audit - all in one place




 MySQL
 PostgreSQL
 MariaDB
Help catch mistakes before they reach production.
Help catch mistakes before they reach production.
Kviklet is built in the open because infra and developer tools should be transparent, inspectable, and shaped by the community.
Keep a record of who accessed a database, what they ran, and when.
Self-host with Docker in your own environment.
Sign in with OIDC or LDAP. SAML is available with Enterprise.
Choose who can request access, who can approve it, and how many approvals are required.
Example policy configuration
Allow access without review where appropriate.
Require a peer or designated reviewer.
Require additional reviewers for access to PII or credit card information.
Apply least-privilege access and approval rules per connection. Keep records of requests, approvals, and database activity to support compliance efforts for:
Pricing
Choose Open Source or Enterprise for your team. Both run in your environment, with professional services and forward-deployed engineering available when you need hands-on help.
Core database access workflows, free to use.
€0
Free to use.
Included in Open Source:
For teams that want to use their own tooling and need advanced access controls, identity integration, and priority support.
€3/ user / month
Billed monthly.
Everything in Open Source, plus:
Prices exclude applicable tax. Choose your number of seats at checkout.
We email your license and setup instructions after payment.
Hands-on help with deployment, custom integrations, and forward-deployed engineering for your team.
How we think about security, engineering culture and open source.
A deep dive on the reasons why software engineers need to have production access to do their work especially in a devops environment and how to manage it securely.

Co-Founder
A guide to setup production ready processes to access databases for a DevOps team. We cover the best practices and tools to use to ensure being secure and compliant.
Co-Founder
Through our research, we’ve identified a spectrum of approaches to managing production database access, ranging from early stage approaches to those adopted by mature organizations

Co-Founder

